Buy nokiaantwerpskatecontest.be ?
We are moving the project
nokiaantwerpskatecontest.be .
Are you interested in purchasing the domain
nokiaantwerpskatecontest.be ?
domain@kv-gmbh.de · 0541-91531010
Buy nokiaantwerpskatecontest.be ?
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **
Similar search terms for Iptables
Top-Angebote
Products related to Iptables:
-
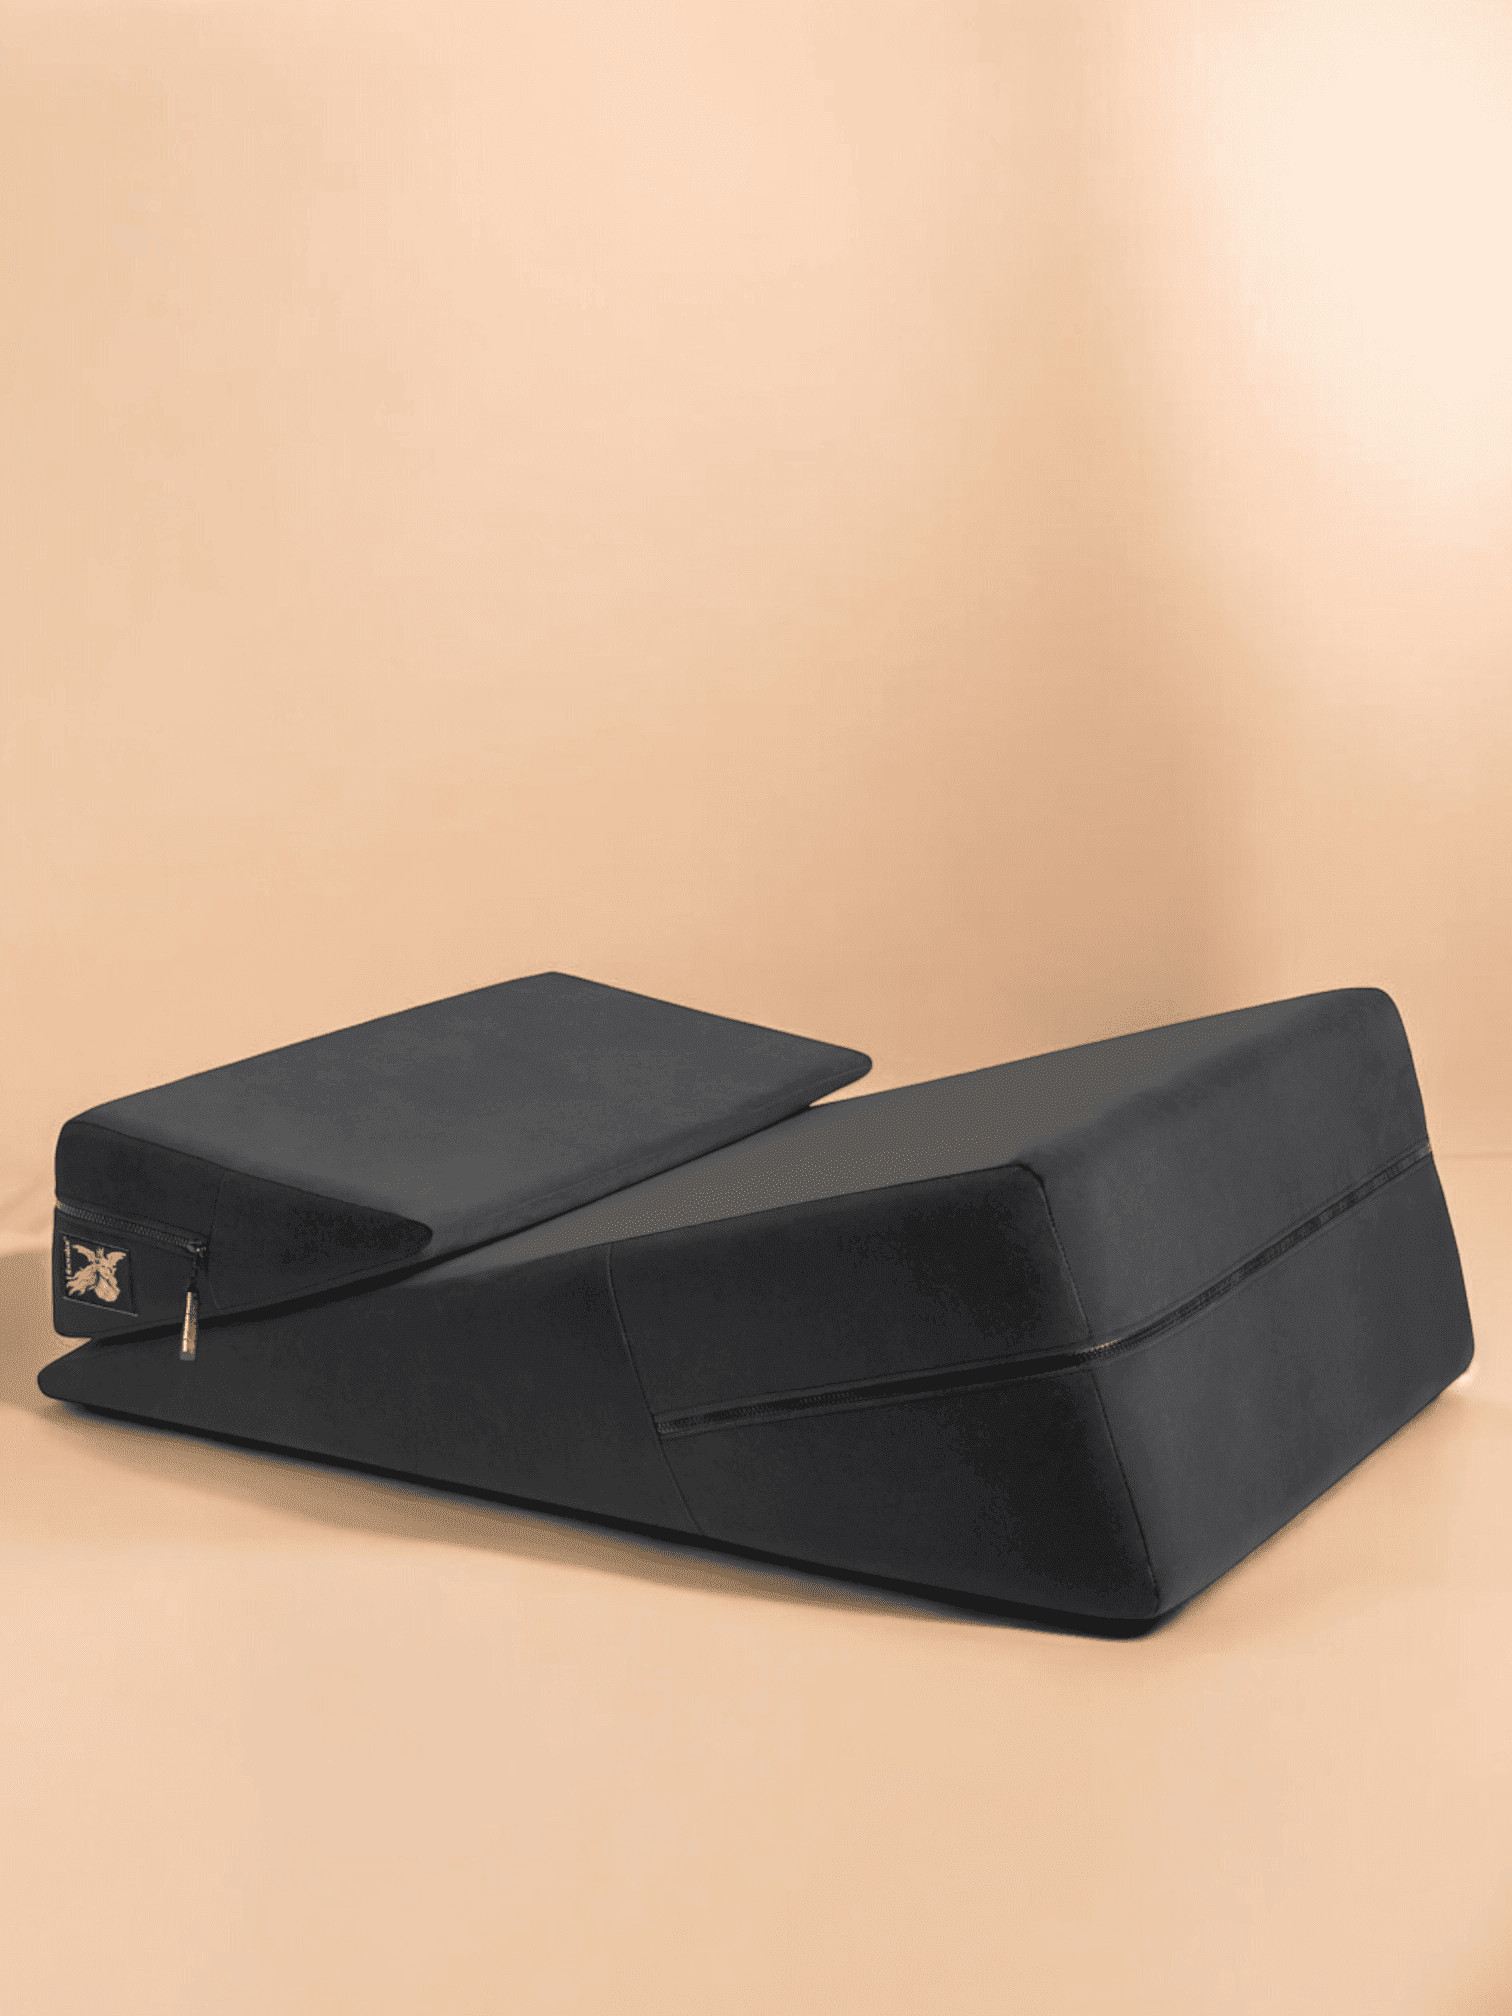
Liberator Kit Bondage avec Coussins "Wedge Ramp Combo"Explorez de nouvelles dimensions du plaisir avec le Kit Bondage avec Coussins "Wedge Ramp Combo" de Liberator. Ce duo de coussins d'amour, conçu pour épouser les formes du corps, vous invite à expérimenter des positions audacieuses et des pénétrations plus profondes. Les coussins cunéiformes369,00 €*Shipping: 0,00 €Secure redirect to the provider
-
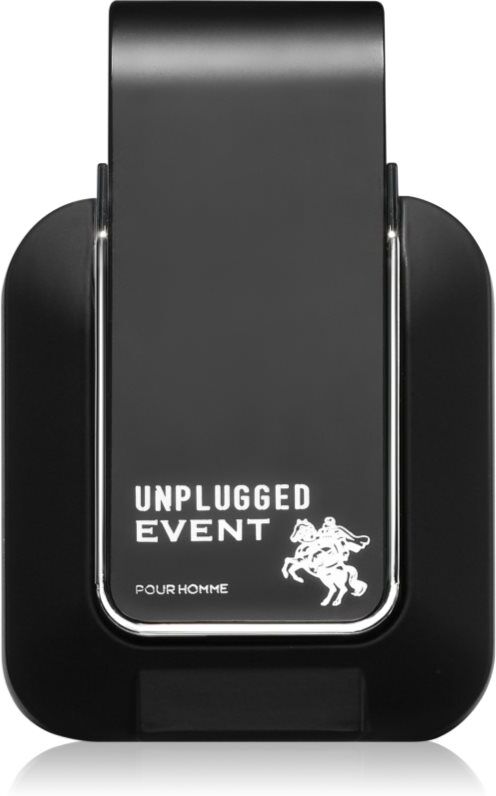
Emper Unplugged Event Eau de Parfum pour homme 80 mlEmper Unplugged Event, 80 ml, Eaux de Parfum pour homme, L'eau de parfum pour homme Emper Unplugged Event sera l’indispensable dont vous ne voudrez plus vous passer. Elle vous séduira dès les premières effluves et deviendra partie intégrante de votre quotidien. parfum fruité parfum floral parfum de musc un parfum plaisant qui ne cessera de vous captiver16,70 €*Shipping: 3,45 €Secure redirect to the provider
-
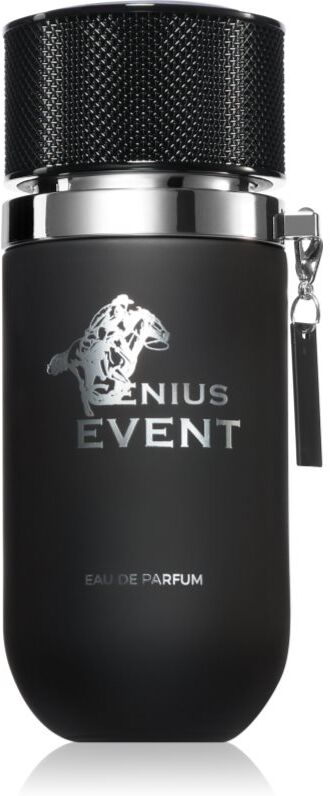
Emper Genius Event Eau de Parfum pour homme 100 mlEmper Genius Event, 100 ml, Eaux de Parfum pour homme, Que vous ayez une réunion d'affaires importante, une fête entre amis ou un dîner avec la femme de votre vie, l'eau de parfum pour homme Emper Genius Event sera votre meilleur atout. Elle vous donnera l’assurance dont vous aurez besoin pour oser vous mettre en valeur. parfum floral parfum boisé il mettra en valeur les hommes qui n'ont pas peur d'être naturels un parfum unique qui se prête aux occasions spéciales18,80 €*Shipping: 3,45 €Secure redirect to the provider

-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **
What tricks are approximately necessary to get sponsored in skateboarding?
To get sponsored in skateboarding, it is important to have a strong and unique style that sets you apart from other skaters. Consistently landing difficult tricks and showcasing creativity in your skating can also help attract the attention of sponsors. Building a strong social media presence and networking within the skateboarding community can also increase your chances of getting sponsored. Ultimately, dedication, passion, and a positive attitude are key factors in catching the eye of potential sponsors. **
Is there also a four-event competition for adults?
Yes, there is a four-event competition for adults in track and field. It is called the decathlon for men and the heptathlon for women. The decathlon consists of ten events, including the 100 meters, long jump, shot put, high jump, 400 meters, 110 meters hurdles, discus throw, pole vault, javelin throw, and 1500 meters. The heptathlon consists of seven events, including the 100 meters hurdles, high jump, shot put, 200 meters, long jump, javelin throw, and 800 meters. These multi-event competitions test the overall athleticism and endurance of the athletes. **
Top-Angebote
Products related to Iptables:
-
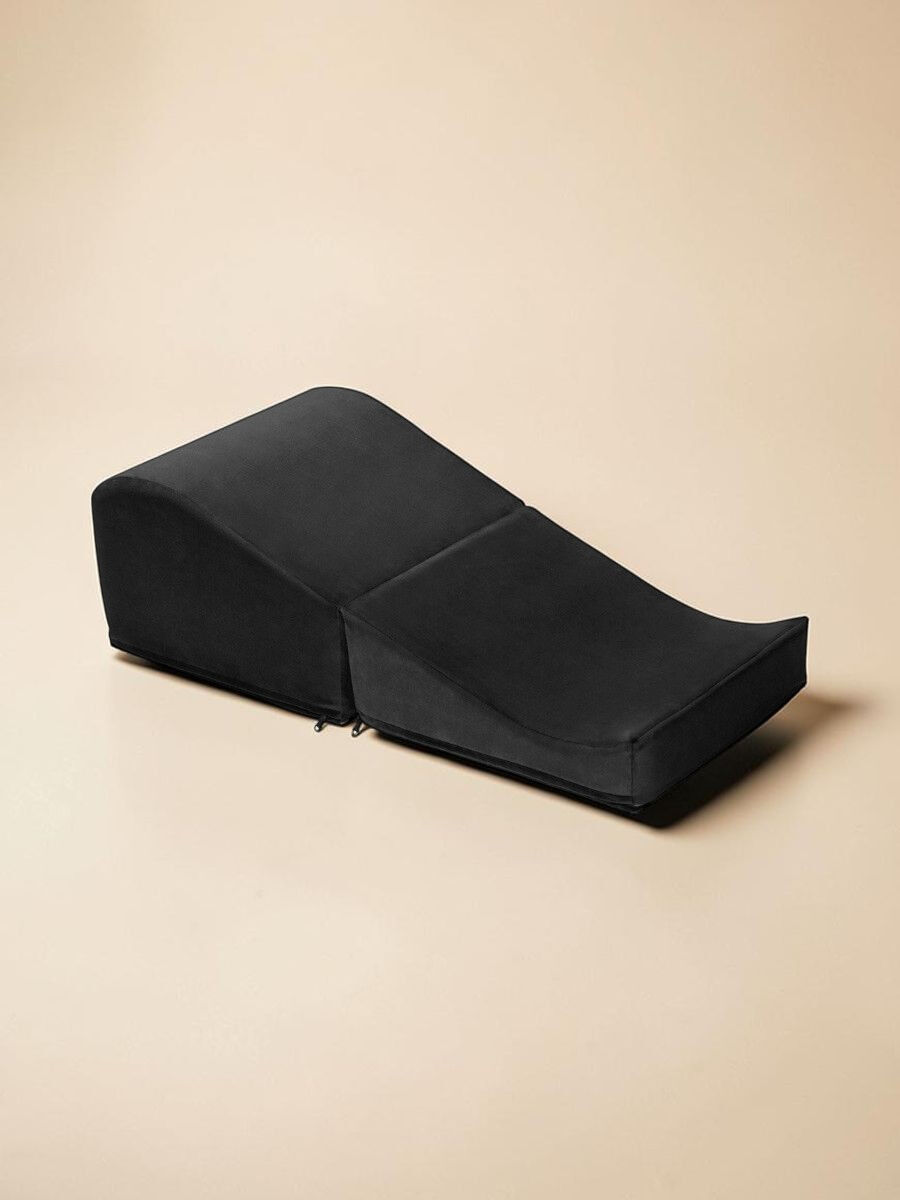
Liberator Flip RampLe Flip Ramp de Liberator attire le regard dès le premier contact. Sa forme intrigante invite à la curiosité et à l’exploration. On le déplie, on l’observe, et déjà les idées fusent. Ce matelas ergonomique s’impose comme un véritable accessoire de confort et de jeu, pensé pour accompagner les219,00 €*Shipping: 0,00 €Secure redirect to the provider
-
Liberator Kit Coussin Wedge Ramp NoirDécouvrez de nouvelles dimensions de plaisir avec le Kit Coussin Wedge Ramp Noir de Liberator. Ces deux coussins d'amour anatomiques transforment chaque moment intime en une expérience inoubliable. Les housses en microfibre, non seulement lavables en machine, adhèrent l'une à l'autre pour garantir269,00 €*Shipping: 0,00 €Secure redirect to the provider
-
Liberator Kit Bondage avec Coussins "Wedge Ramp Combo"Explorez de nouvelles dimensions du plaisir avec le Kit Bondage avec Coussins "Wedge Ramp Combo" de Liberator. Ce duo de coussins d'amour, conçu pour épouser les formes du corps, vous invite à expérimenter des positions audacieuses et des pénétrations plus profondes. Les coussins cunéiformes369,00 €*Shipping: 0,00 €Secure redirect to the provider
-
Emper Unplugged Event Eau de Parfum pour homme 80 mlEmper Unplugged Event, 80 ml, Eaux de Parfum pour homme, L'eau de parfum pour homme Emper Unplugged Event sera l’indispensable dont vous ne voudrez plus vous passer. Elle vous séduira dès les premières effluves et deviendra partie intégrante de votre quotidien. parfum fruité parfum floral parfum de musc un parfum plaisant qui ne cessera de vous captiver16,70 €*Shipping: 3,45 €Secure redirect to the provider
-
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
-
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
Similar search terms for Iptables
-
Emper Genius Event Eau de Parfum pour homme 100 mlEmper Genius Event, 100 ml, Eaux de Parfum pour homme, Que vous ayez une réunion d'affaires importante, une fête entre amis ou un dîner avec la femme de votre vie, l'eau de parfum pour homme Emper Genius Event sera votre meilleur atout. Elle vous donnera l’assurance dont vous aurez besoin pour oser vous mettre en valeur. parfum floral parfum boisé il mettra en valeur les hommes qui n'ont pas peur d'être naturels un parfum unique qui se prête aux occasions spéciales18,80 €*Shipping: 3,45 €Secure redirect to the provider
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **
-
What tricks are approximately necessary to get sponsored in skateboarding?
To get sponsored in skateboarding, it is important to have a strong and unique style that sets you apart from other skaters. Consistently landing difficult tricks and showcasing creativity in your skating can also help attract the attention of sponsors. Building a strong social media presence and networking within the skateboarding community can also increase your chances of getting sponsored. Ultimately, dedication, passion, and a positive attitude are key factors in catching the eye of potential sponsors. **
-
Is there also a four-event competition for adults?
Yes, there is a four-event competition for adults in track and field. It is called the decathlon for men and the heptathlon for women. The decathlon consists of ten events, including the 100 meters, long jump, shot put, high jump, 400 meters, 110 meters hurdles, discus throw, pole vault, javelin throw, and 1500 meters. The heptathlon consists of seven events, including the 100 meters hurdles, high jump, shot put, 200 meters, long jump, javelin throw, and 800 meters. These multi-event competitions test the overall athleticism and endurance of the athletes. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.